WhoopShop — protecting an online store from bots
For the WHOOP fitness band store, we built a custom smart captcha that stops bots without getting in shoppers' way, fixed errors in how the website worked and hardened its security, with no changes to the storefront design.
Challenge
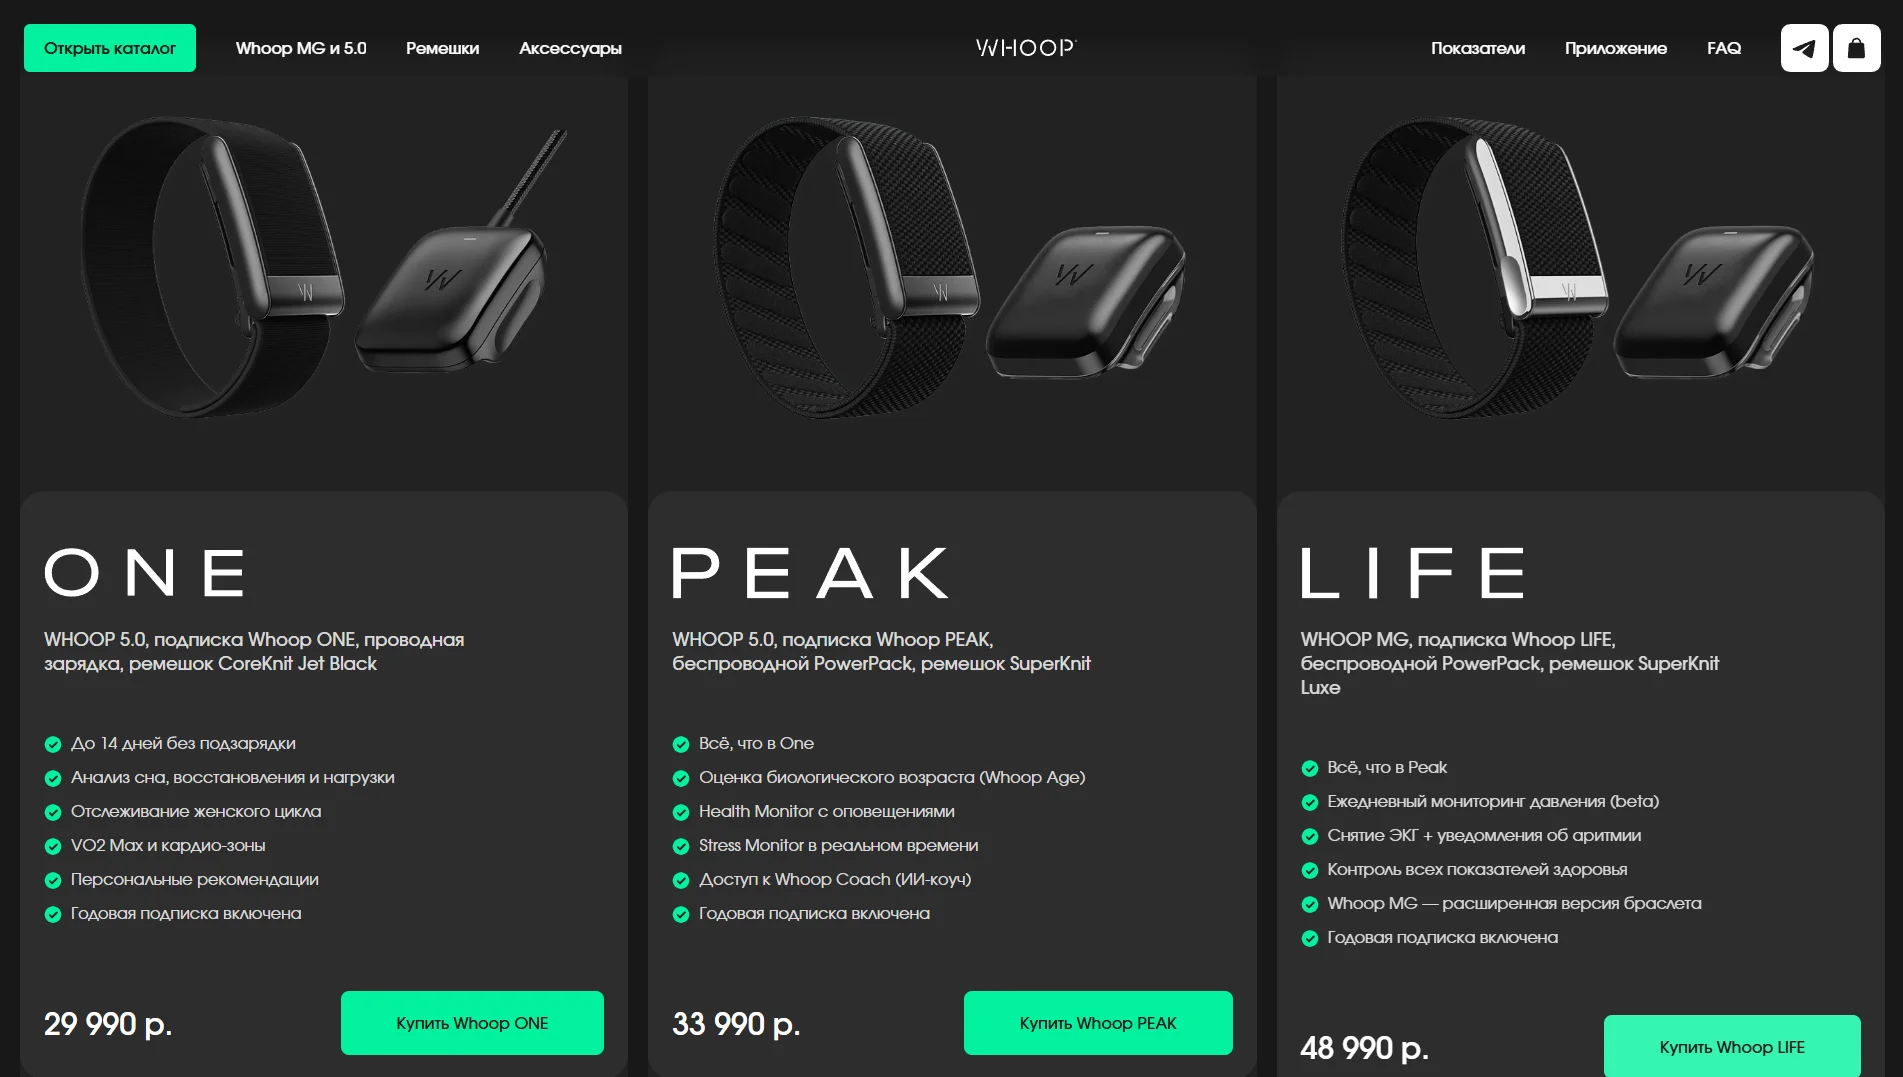
WhoopShop is an online store for WHOOP fitness bands: WHOOP 5.0 and WHOOP MG trackers, ONE, PEAK and LIFE memberships, straps, chargers and a trade-in for older models. Customers place orders, leave requests and ask questions through forms on the website, so their reliability directly affects sales.
The store's forms had become a target for automated traffic. Bots sent fake requests, cluttered the inquiry database and took up the managers' time: instead of working with customers, the team had to separate real requests from junk by hand.
Off-the-shelf solutions did not fit. A standard image-recognition captcha annoys a person at the last step before buying and hurts sales, while simple checks are passed by modern bots automatically. The store needed protection that is invisible to a shopper and impassable for a script.
At the same time, errors had piled up on the website, and some user flows worked unreliably. For an online store, every such failure means a lost order, an extra support request and less trust in the shop where a person was about to spend money.
On top of that, a wave of bots is rarely just spam: the same traffic often probes forms and service URLs for vulnerabilities. So the task went beyond a captcha. The whole website needed stronger protection, and the work had to be careful, leaving the design and the familiar path to an order untouched.
Solution
We started with an audit: where the automated traffic comes from, which forms and flows it uses and where the website breaks. That gave us a work map across three lines: bot protection, bug fixing and security.
The core of the project is a custom smart captcha. It evaluates visitor behaviour and technical signs of the session in the background: a real shopper passes the check without noticing it, while suspicious traffic gets a challenge a script cannot solve. The result is verified on the server, so a bot cannot submit a request by bypassing the captcha with a direct call.
In parallel, we fixed errors in how the website worked, closed the weak spots found during the audit and then tested the key customer flows, from the catalog to checkout. All changes were made under the hood: the design and the storefront customers know stayed the same.
Traffic and vulnerability audit
We analysed where the automated traffic comes from, which forms it attacks and which signs set it apart from human behaviour. At the same time we listed the website's errors and weak spots, and that list became the plan for all three lines of work.
A custom smart captcha
Instead of an off-the-shelf widget, we built our own captcha. It takes visitor behaviour and technical signs of the session into account: a real shopper passes the check without noticing it, while suspicious traffic gets a task a script cannot solve.
Server-side verification
The check result is confirmed on the server, not only in the browser. That is why a bot cannot submit a request by bypassing the captcha with a direct call, and the protection sits on the forms the store uses to receive orders and inquiries.
Fixing the website's errors
We found and removed the errors that made some user flows unreliable. Every fix was then tested on the real customer path: the catalog, a product page, a request form and the checkout itself.
Hardened security
We closed the weak spots found during the audit and limited the room for automated brute force and spam. The protection works at the application level and complements the infrastructure protection that already stood in front of the store.
No change to the design
All changes were made under the hood: the storefront, catalog and checkout stayed exactly as customers know them. The store kept running as usual, and the WhoopShop team got a website that filters out bots on its own.
Results
The project's key outcomes in numbers.
- 24/7Form protection from bots
The smart captcha works around the clock and stops automated traffic before it reaches the inbox.
- 3Lines of work
Bot protection, bug fixing and hardened security, all in one project.
- 0Changes to the design
Everything was done under the hood: customers use the store exactly as before.
- CustomIn-house captcha
Not a standard third-party widget, but a captcha written for this store's own flows.
Design & interfaces
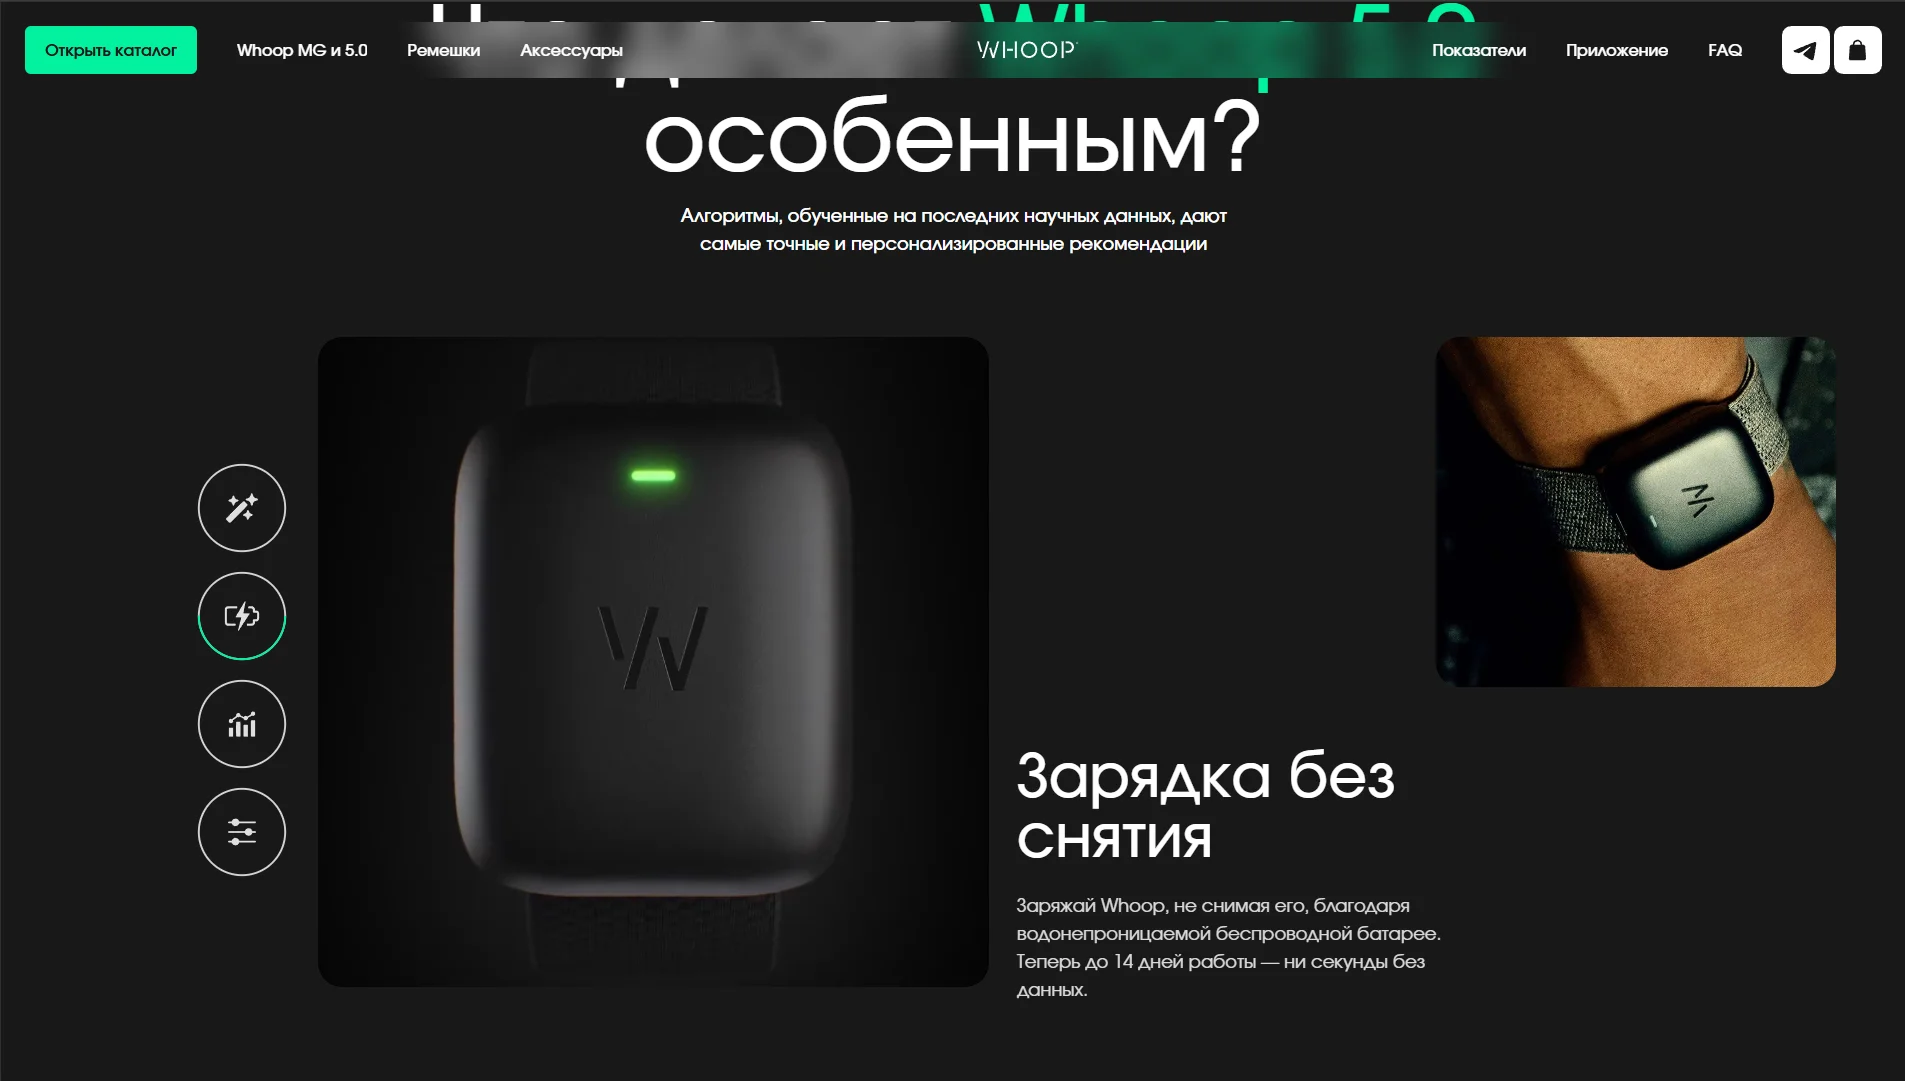
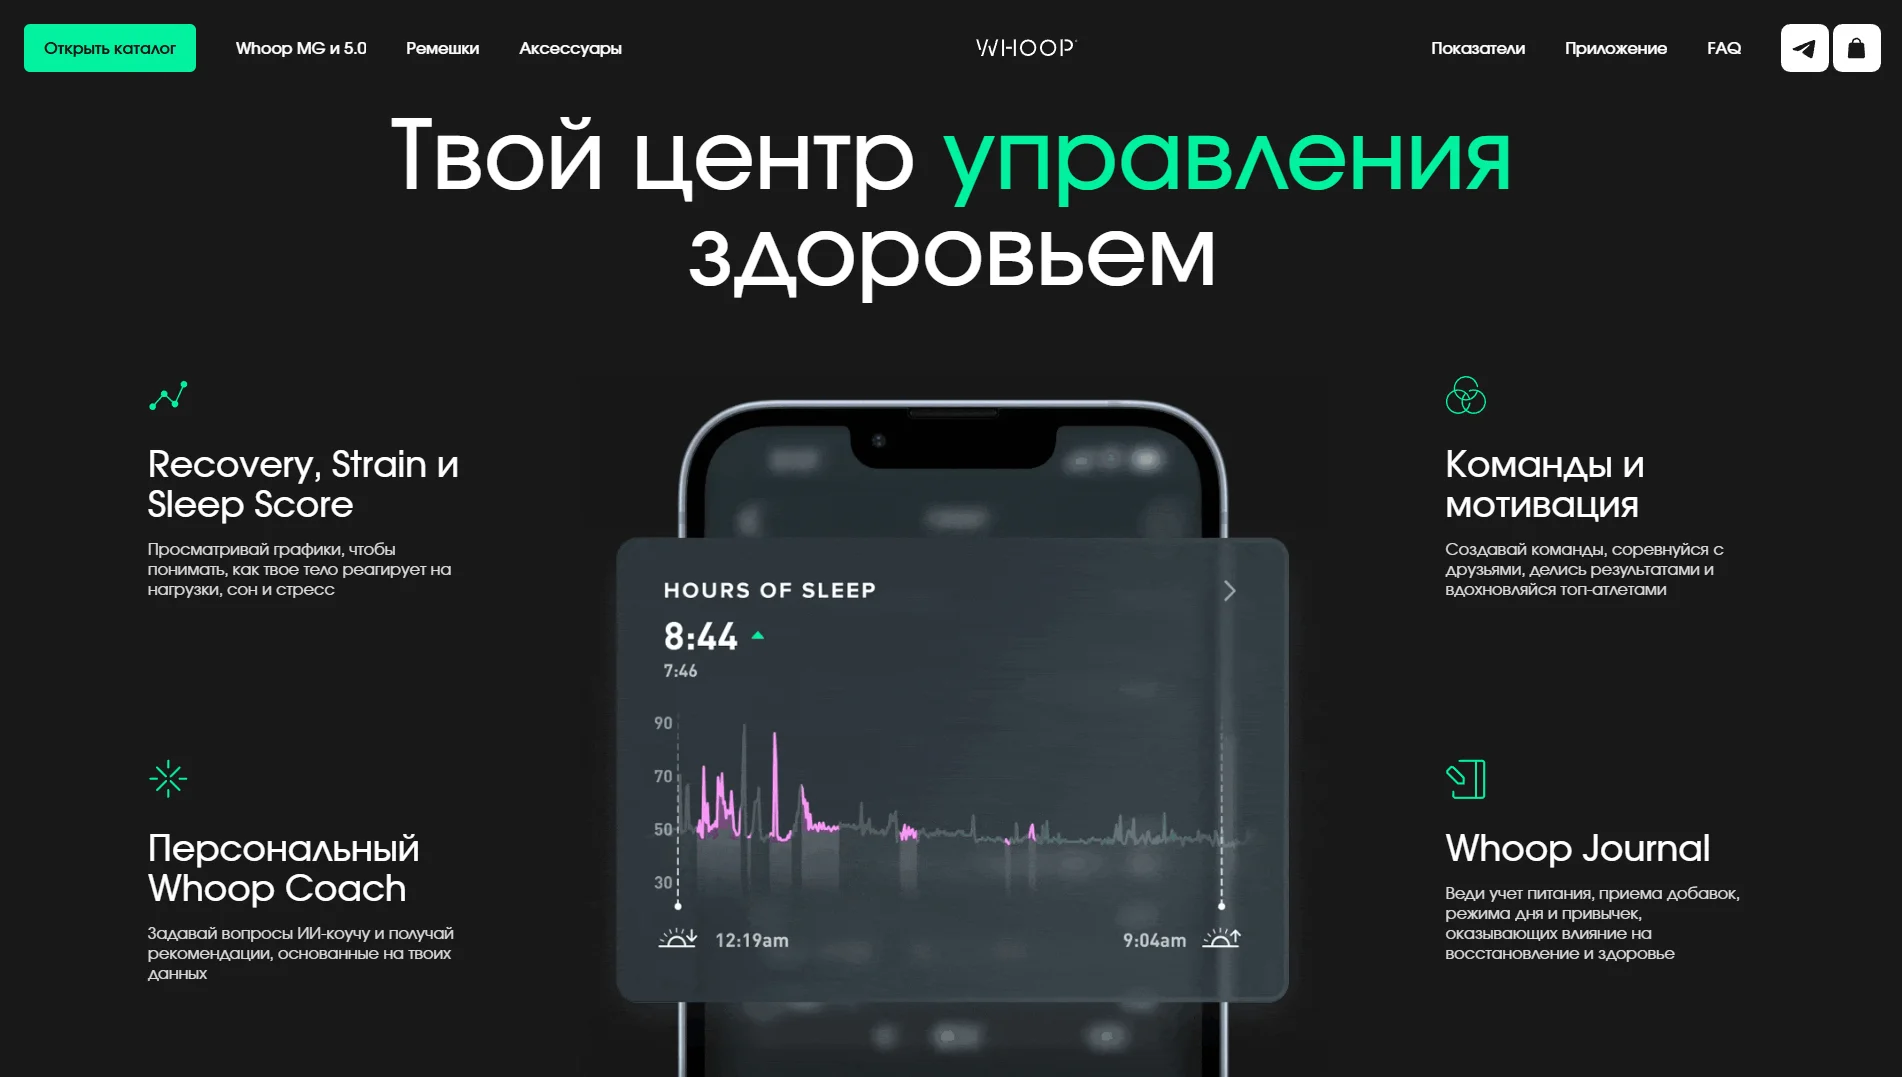
Key screens and interfaces of the project.
Project tech stack
The stack we used to build the solution for the client's task.
- PHP
- Laravel
- JavaScript
Similar cases
Ready to become the next case?
Tell us about your task — a manager will assemble the team, calculate the estimate and send a proposal within the first hour after the request. No obligations, no drip campaigns.